Coinbase Says Funds Safe After Unexpected Vendor Data Exposure
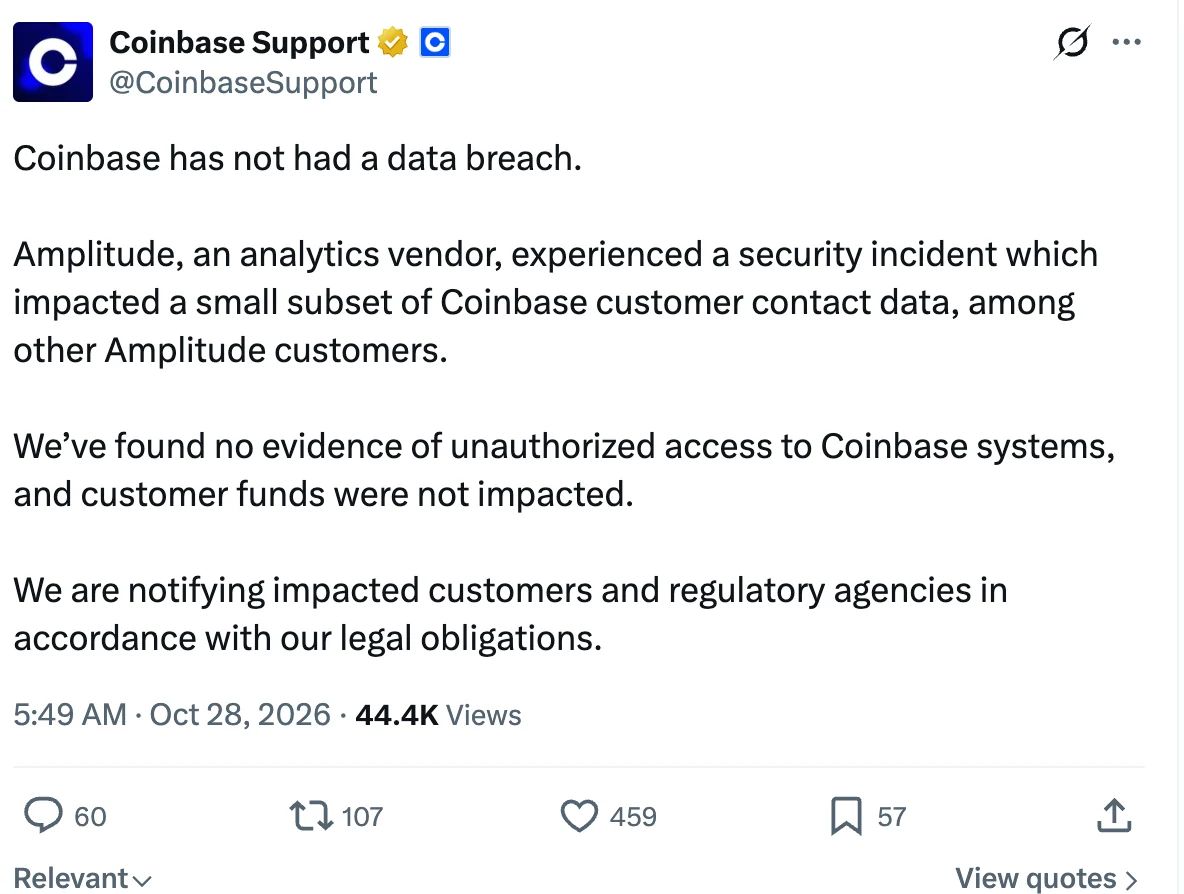
Photo: CoinCentral
TLDR Coinbase denied reports of an internal hack after Amplitude exposed some customer contact information. Amplitude’s security incident reportedly exposed email addresses and phone numbers belonging to exchange customers. SlowMist circulated an unverified claim involving more than 70,000 Coinbase users, although the exchange has not confirmed the figure. Affected customers are receiving email notifications as Coinbase reports the incident to relevant authorities. Separate security incidents also affected Bithumb, Daishin Securities and Mirae Asset Global Investments in South Korea. Coinbase has rejected reports that hackers accessed its systems after customer contact details were exposed through Amplitude, an analytics provider.
Source: CoinCentral